 Nomid
This guide shows how to install Cloudflare One Agent (com.cloudflare.cloudflareoneagent), the Android app for Cloudflare One (Cloudflare Zero Trust), on company devices managed by Nomid MDM, and how to configure it with managed configurations. Cloudflare calls these values deployment parameters. With them, the app signs in to your Zero Trust organization, stays connected, and shows your support contact. You can also choose which apps send their traffic through Cloudflare.
Cloudflare One Agent replaces the 1.1.1.1 app (com.cloudflare.onedotonedotonedotone) for Zero Trust. Cloudflare no longer supports the 1.1.1.1 app for Zero Trust features. If your devices still use it, see Moving from the 1.1.1.1 app before you start.
The steps use the Policy 2.0 editor. In the Classic editor, the same fields open from the gear on the app card; see 4.1 Tablet policies — Classic.
Risk: Cloudflare One Agent settings change how the device reaches the network. A locked switch, a service mode, a per-app list or an always-on VPN that blocks other traffic can cut access to company apps and to device management. A malformed endpoint value can stop the app from reading the whole configuration. Test every change on a pilot policy with one device before you link the policy to the fleet.
Before you begin
- An Android Enterprise company in Nomid MDM with fully managed or work profile devices, and the Edit policy permission for the policy you will change.
- A Cloudflare Zero Trust organization and access to the Cloudflare One dashboard. You need your team name (the organization that people sign in to) and device enrollment permissions that let your users, or a service token, enroll devices.
- VPN settings set to Allowed under Connectivity in the policy. Cloudflare One Agent runs as a VPN on Android, and while VPN settings is Blocked the device can stop it from getting VPN access. Allowed also lets people on the device add, edit or remove VPNs.
- A pilot policy linked to a single test device, so a wrong value affects only that device.
Add Cloudflare One Agent to the policy
- In the Nomid Portal, open Policies and select the pilot policy.
- Open the Apps & experience tab and select Apps in this policy.
- Select Add App. Choose Add via Package, type
com.cloudflare.cloudflareoneagentand confirm that Cloudflare One Agent appears under the field. Select Add. You can also choose Add via Play Store and search for Cloudflare One Agent in managed Google Play.
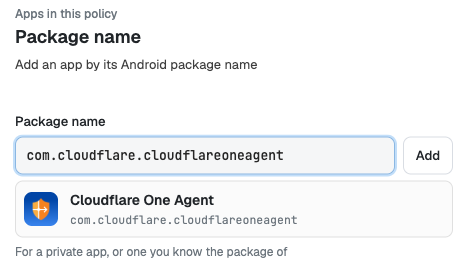
Type the package name and check that the match is Cloudflare One Agent before you add it.
- Cloudflare One Agent now appears in the list with the Configurable badge, which means the app publishes managed configurations. The pane footer shows Edited. Save the policy to apply until you save. The installation choice next to the app starts as Required, which installs the app and keeps it on the device. Optional, Blocked and the other app controls are described in 4. Policies — Policy 2.0.
Open the managed configurations
Select the gear next to Cloudflare One Agent in the list. The Managed configurations editor lists every field that the installed version publishes. Google Play supplies this list from the app, so it can change when Cloudflare releases a new version.
Cloudflare One Agent publishes a single list, App config list (app_config_bundle_list). Each item in the list holds the settings for one Zero Trust organization:
- Select Add New Item. Item 1 opens with every field for that organization.
- Fill in the fields you need, starting with Organization.
- Most fleets need only Item 1. Cloudflare's Intune guide uses one item per organization. Whether people can switch between several items in the Android app is not confirmed in Cloudflare's documentation; if you add more, give each a Display name and test it on the pilot device.
The editor works the same way for every field:
- Each field shows its title, a description written by Cloudflare, and the key name. The button next to the key copies a link to that field.
- Default value shows the value the app declares. It is information only: the editor does not send it.
- Not Set sends nothing for that field, so the app keeps its own behavior.
- Use the filter box to find a key, and All, Filled or Not Filled to review what you have entered. Expand All and Collapse All open or close every item.
- The X on an item removes that organization from the list. Delete all configurations clears every Cloudflare One Agent value in this policy.
- Save keeps your values in the policy edit; Cancel leaves the editor without them. Neither sends anything to devices until you save the policy.
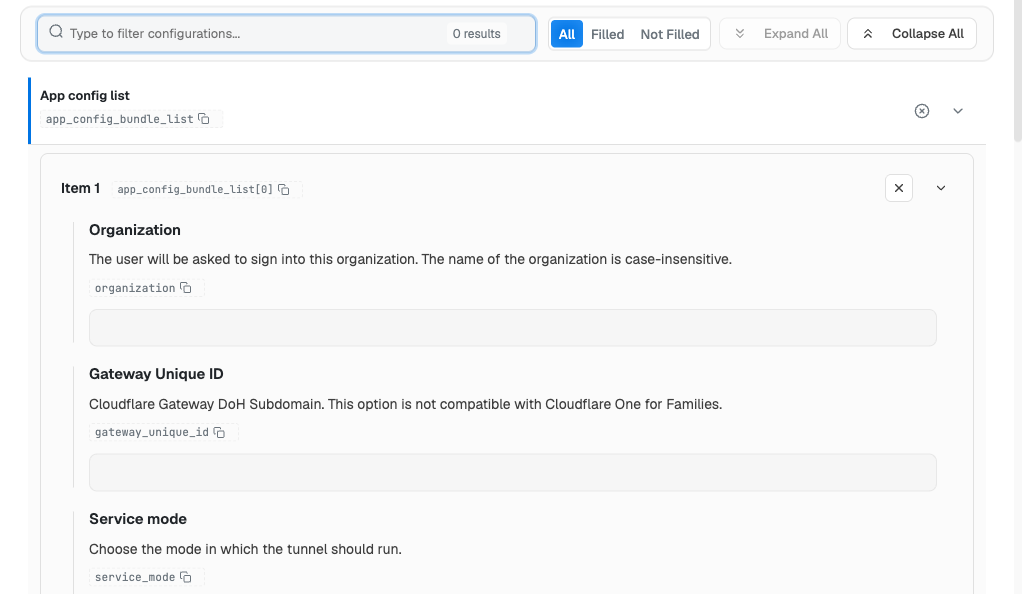
Every setting sits inside an item of App config list. Leave a field on Not Set unless you need it.
Managed configuration keys
The tables follow the field titles shown in the editor, all inside one item of App config list. Toggle fields offer Not Set, Enabled and Disabled. Leaving any field on Not Set keeps the Cloudflare default. Values, defaults and version numbers come from Cloudflare's deployment parameters unless a row says otherwise. Values you set here take precedence over the matching device settings in the Cloudflare One dashboard.
Organization and sign-in
| Field and key | Value | Effect |
|---|---|---|
Organization (organization) |
Your team name, for example example-corp |
The app asks people to sign in to this organization. The name is not case-sensitive. |
Display name (display_name) |
Text | The name people see for this organization in the app. Cloudflare requires it when a configuration lists several organizations. |
Auth client ID (auth_client_id) |
Service token client ID | With Auth client secret, enrolls the device with a service token instead of a person signing in. See the warning below. |
Auth client secret (auth_client_secret) |
Service token client secret | The secret paired with Auth client ID. |
Unique client ID (unique_client_id) |
UUID | Assigns an identifier to the device for Cloudflare's device UUID posture check. Because a policy sends the same value to every device in it, use it only on a policy with one device. |
Compliance Environment (environment) |
normal or fedramp_high |
Connects the app to the matching Cloudflare environment. Leave it on Not Set unless your organization runs in FedRAMP High. Version 2.5.1 or later. |
Service token warning: anyone who can view the policy in the Portal can read the client ID and secret, and a policy sends the same token to every device in it. Cloudflare requires the token to be allowed by a Service Auth rule in your device enrollment permissions; an Allow rule does not work. Give the token the shortest duration that covers the rollout, revoke it in the Cloudflare One dashboard when devices are enrolled, and never show it in screenshots or support tickets.
Connection
| Field and key | Value | Effect |
|---|---|---|
Service mode (service_mode) |
warp (default), 1dot1, postureonly |
warp sends network traffic and DNS through Cloudflare. 1dot1 sends only DNS. postureonly only reports device posture. Cloudflare limits tunnelonly (traffic only) and proxy (local proxy) to Windows, Linux and macOS, so do not use them on Android. Type the value exactly as shown. |
Switch Locked (switch_locked) |
Enabled, Disabled | Enabled prevents people from turning off the connection switch. Disabled, the default, leaves the switch to the person. Cloudflare says new deployments must also set Auto Connect. |
Auto Connect (auto_connect) |
Number from 0 to 1440 |
0 lets the switch stay off until the person turns it back on. 1 to 1440 turns the switch back on automatically after that many minutes. |
Gateway Unique ID (gateway_unique_id) |
Your Gateway DoH subdomain | Sends all DNS queries to that Gateway DNS location. Needed only without a team name or when your organization has several DNS locations; otherwise the app uses your default location. Not compatible with Cloudflare One for Families. |
WARP tunnel protocol (warp_tunnel_protocol) |
masque or wireguard |
Chooses the tunnel protocol. Leave it on Not Set to use the protocol set in the Cloudflare One dashboard. |
Enable Post-quantum encryption (enable_post_quantum) |
Enabled, Disabled | Turns post-quantum encryption on or off for the tunnel. It needs the MASQUE protocol, so do not combine it with wireguard in WARP tunnel protocol. Version 2.4 or later. |
DoH outside tunnel (doh_outside_tunnel) |
Enabled, Disabled | Sends DNS over HTTPS traffic outside the tunnel. The app's description says your firewall must then allow .cloudflare-gateway.com. Cloudflare's parameters page does not document this key, so leave it on Not Set unless Cloudflare support recommends it. |
Enable PMTUD (enable_pmtud) |
Enabled, Disabled | Path MTU Discovery finds the largest packet size the network allows, to improve connection performance. |
Apps that use the tunnel
List of application package names that should be tunneled through the WARP service (tunneled_apps) is a list inside the item. Select Add New Item inside it once for each app:
| Field and key | Value | Effect |
|---|---|---|
Tunneled application package name (app_identifier) |
Package name, for example com.android.chrome |
Chooses an Android app that sends its traffic through the tunnel. |
Is this the browser? (is_browser) |
Enabled, Disabled | Enabled tells the app to open this browser instead of the default one for re-authentication and Gateway block notifications. Without it, the app does not treat the package as a browser. |
Cloudflare documents this list in its Intune guide, which says per-app routing on Android needs Cloudflare One Agent 2.3 or later. Test on the pilot device which apps reach resources behind Cloudflare with the list in place, including one app outside the list.
Endpoint overrides
| Field and key | Value | Effect |
|---|---|---|
Api endpoint (override_api_endpoint) |
IP address | Replaces the address the app uses for Cloudflare's API. |
DoH endpoint (override_doh_endpoint) |
IP address | Replaces the DNS over HTTPS address. Applies only when Service mode is 1dot1. |
Warp endpoint (override_warp_endpoint) |
IP address and port, for example 203.0.113.10:443 |
Replaces the tunnel address. |
Leave these fields on Not Set unless Cloudflare asks you to set them. Cloudflare warns that one malformed value makes the app ignore the whole configuration.
What people see in the app
| Field and key | Value | Effect |
|---|---|---|
Show onboarding (onboarding) |
Enabled, Disabled | Disabled skips the onboarding screens where people review the privacy policy when the app first opens. The default is Enabled. Check your own privacy obligations before you hide them. |
Support URL (support_url) |
https:// or mailto: address |
Opens this address when people use Send feedback in the app. |
Use in-app WebView for authentication (use_in_app_webview) |
Enabled, Disabled | Opens the Zero Trust sign-in inside the app instead of the default browser. Cloudflare requires it when always-on VPN runs in lockdown mode, which in the Portal is Block connections without the VPN. |
Some parameters on Cloudflare's page, such as proxy_port, allow_updates and the multi-organization configs list used on desktop systems, do not appear in the editor because the Android app does not publish them. The editor sends only the fields the app declares.
Sample policy for shared frontline devices
This example keeps shared devices connected to the company organization with a simple app. Replace example-corp with your team name and the support details with your own values. All values go in Item 1.
| Field | Value | Why |
|---|---|---|
| Organization | example-corp |
The app signs in to your organization only. |
| Display name | Example Corp |
Shows a clear name in the app. |
| Service mode | warp |
Sends DNS and network traffic through Cloudflare. |
| Switch Locked | Enabled | Staff cannot turn the connection off by mistake. |
| Auto Connect | 1 |
If the connection is off, it turns back on after one minute. |
| Show onboarding | Disabled | Skips the privacy policy screens on shared devices, if your privacy obligations allow it. |
| Support URL | https://help.example.com/vpn |
Opens your help page from Send feedback. |
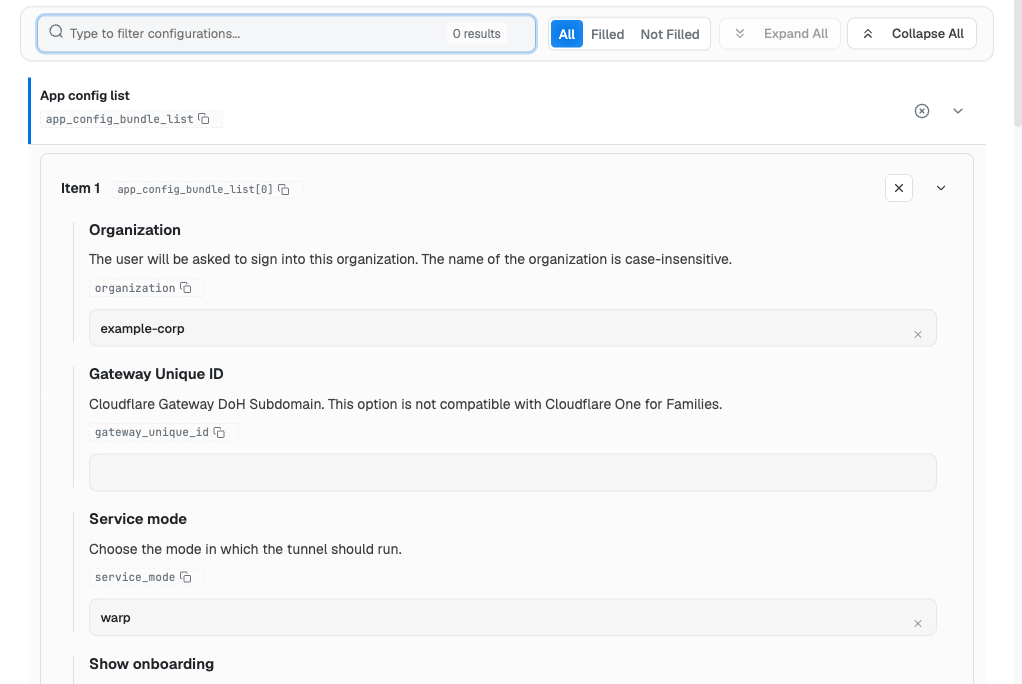
Fill in the item, then use Filled to review every value before you save.
Save and apply the policy
- In the managed configurations editor, select Save, then Done in the apps pane.
- Select Save in the policy header, review the list of changes and confirm.
- Linked devices receive the policy when they synchronize. Cloudflare One Agent reads the new values from the device's managed configuration.
Optional: always-on VPN
To have Android start Cloudflare One Agent at boot and keep it running, choose it as the VPN app under Connectivity > Traffic routing > Always-on VPN, as described in 4. Policies — Policy 2.0. If you turn on Block connections without the VPN, also set Use in-app WebView for authentication to Enabled; Cloudflare requires it in that mode. Leave the block off until the pilot device signs in and reconnects reliably. With it on, a device that is signed out has no network, which can also stop policy updates.
Verify on the device
- In Devices, open the pilot device, run a synchronization and confirm that Cloudflare One Agent is installed.
- On the device, open Cloudflare One Agent. With Organization set, it goes straight to your organization's sign-in. With a service token, it enrolls without asking anyone to sign in.
- Sign in through your identity provider. With Switch Locked set to Enabled, the switch cannot be turned off.
- In the Cloudflare One dashboard, open Team & Resources > Devices and confirm that the device appears.
- From the device, open an internal address or a site your Gateway policies filter, to confirm traffic goes through Cloudflare. If you set tunneled apps, test one listed app and one app outside the list.
Troubleshooting
| Problem | Likely cause | What to do |
|---|---|---|
| No Configurable badge or no fields in the editor | The package was not resolved from Google Play, or the list has not loaded. | Remove the app, add it again with com.cloudflare.cloudflareoneagent and check that Cloudflare One Agent appears as the match. |
| The fields are missing | No item has been added to App config list. | Select Add New Item under App config list. |
| A parameter from Cloudflare's documentation is missing | The Android app does not publish it. | Use only the fields the editor lists. |
| Values do not reach the app | The policy was not saved, the device has not synchronized, or a value is malformed. | Save the policy, synchronize the device in Devices and check the endpoint fields for typing errors. |
| The app asks for an organization | Organization is empty, or it is outside Item 1. | Enter the team name in the Organization field of the item. |
| Enrollment with the service token fails | The token is expired or revoked, or device enrollment permissions use Allow instead of Service Auth. | Check the token and the rule in the Cloudflare One dashboard. |
| The app says it needs VPN access | VPN settings is Blocked in the policy, or another VPN is running. | Set VPN settings to Allowed under Connectivity and save the policy. Disconnect any other VPN, then reopen the app. |
| An app cannot reach internal services | Tunneled apps is filled in and the app is not on the list. | Add its package name to the list and save the policy. |
| Sign-in fails with always-on VPN | Block connections without the VPN is on and in-app WebView is off, which Cloudflare does not support. | Set Use in-app WebView for authentication to Enabled, or turn the block off. |
| The device has no internet after enabling always-on VPN | Block connections without the VPN is on and the app is signed out or disconnected. | Turn the block off in the policy, save, and sign in again. |
Moving from the 1.1.1.1 app
If your devices run the 1.1.1.1 app for Zero Trust, follow Cloudflare's migration guide:
- Update the 1.1.1.1 app to version 6.29 or later, so both apps can stay installed during the move.
- Add Cloudflare One Agent to the policy and copy your existing values into its App config list item. Copy only the deployment parameters, not the app's package name. Cloudflare's guide describes no key renames.
- Only one of the two apps can connect at a time. On Android, people sign in again in Cloudflare One Agent. The device appears in the dashboard with a new device ID, and the old registration stays as an inactive device.
- Once the devices are connected, set the 1.1.1.1 app to Blocked or remove it from the policy. People can keep it for personal browsing on devices where you allow it.
Undo the configuration
- To stop enforcing one value, open the field and choose Not Set, or clear the text, then save the policy.
- The X on an item removes that organization. Delete all configurations removes every Cloudflare One Agent value from this policy after you save it.
- To remove the app, change its installation to Blocked, as described in 4. Policies — Policy 2.0, and save. Revoke any service token you distributed.